DevOps tutorials from real setups
Step-by-step guides on AWS, Terraform, CI/CD and Kubernetes. Every post is based on infrastructure I actually run.
All posts
gp2 vs gp3: switch EBS volumes, save 20%, no downtime
gp2 vs gp3 compared: gp3 costs 20% less per GB and gives 3,000 IOPS at any size. Find every gp2 volume, switch it live, and avoid the big-volume IOPS trap.
Base64 is not encryption: Kubernetes Secrets and JWT mistakes
Base64 is encoding, not encryption, so Kubernetes Secrets and JWT payloads are readable by anyone. What that means, how to decode safely, and safer options.
EventBridge cron expressions vs cron: the 6-field trap
An EventBridge cron expression has 6 fields, a required question mark and different day numbers. How it differs from cron, CronJobs and GitHub Actions.
How to plan VPC CIDR ranges so you never have to rebuild
VPC CIDR planning in plain steps: pick a range and subnet sizes that leave room to grow, avoid overlaps, and allow for the 5 IPs AWS reserves per subnet.
3 YAML mistakes that break Kubernetes and GitHub Actions deploys
Three YAML mistakes that break Kubernetes and GitHub Actions deploys: tabs and indentation, values that turn into the wrong type, and files nobody validated.
Does AWS charge for stopped instances? 3 hidden charges
Does AWS charge for stopped instances? Not for compute, but their EBS volumes and public IPs keep billing. Find them, and idle IPs, with three CLI commands.
Case study: GitHub Actions OIDC replaced a startup's AWS keys
A GitHub Actions OIDC case study: a small team kept long-lived AWS keys in CI and never rotated them. How I moved them to OIDC in one day, and what changed.
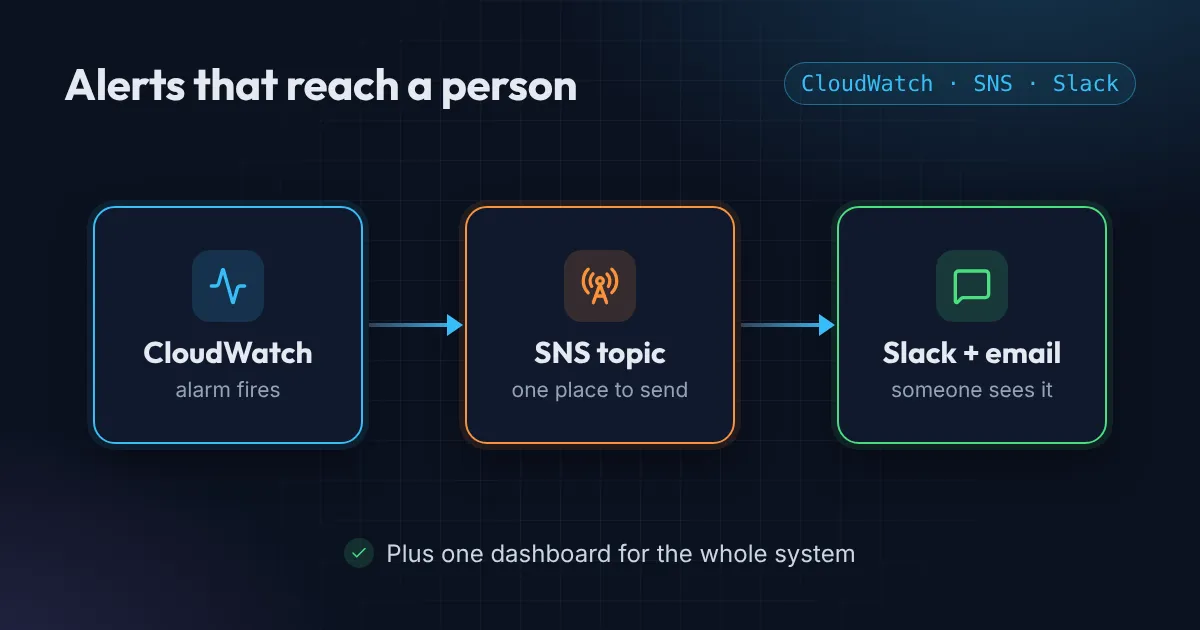
AWS alerts: know about outages before your customers do
Set up AWS alerts that reach you first. No alerts, alerts nobody sees, no dashboard: a small CloudWatch, SNS and Slack setup fixes all three, no new tool.
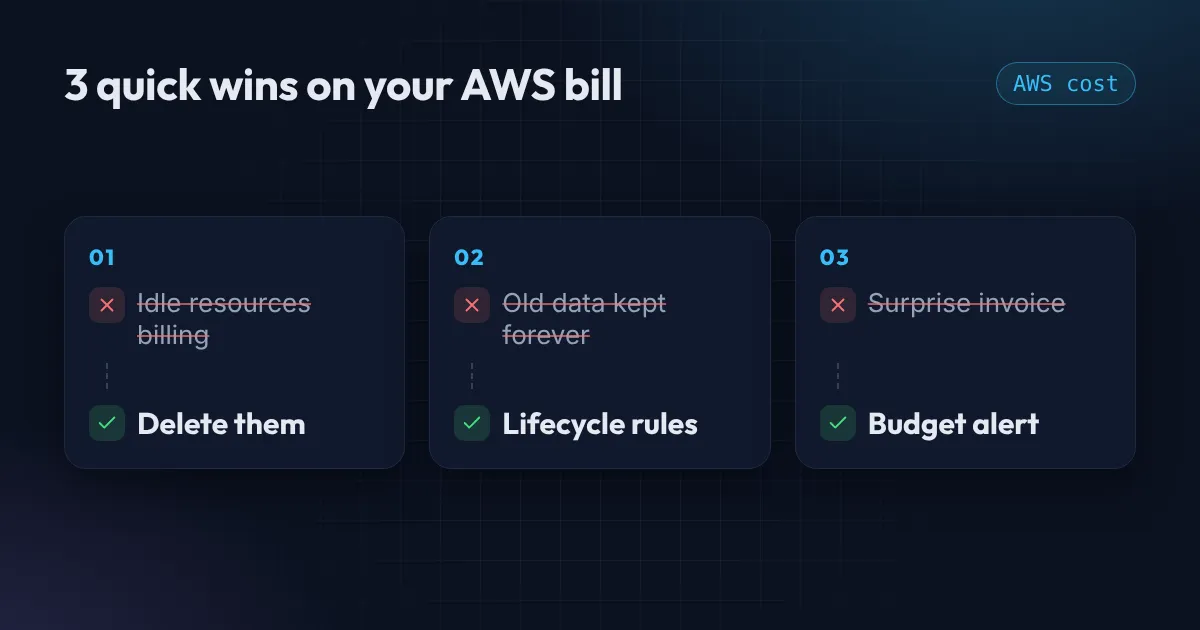
How to reduce your AWS bill: 3 quick wins that break nothing
Reduce AWS costs without touching your app: delete idle resources that still bill you, let old data expire, and set a budget alert before the invoice.
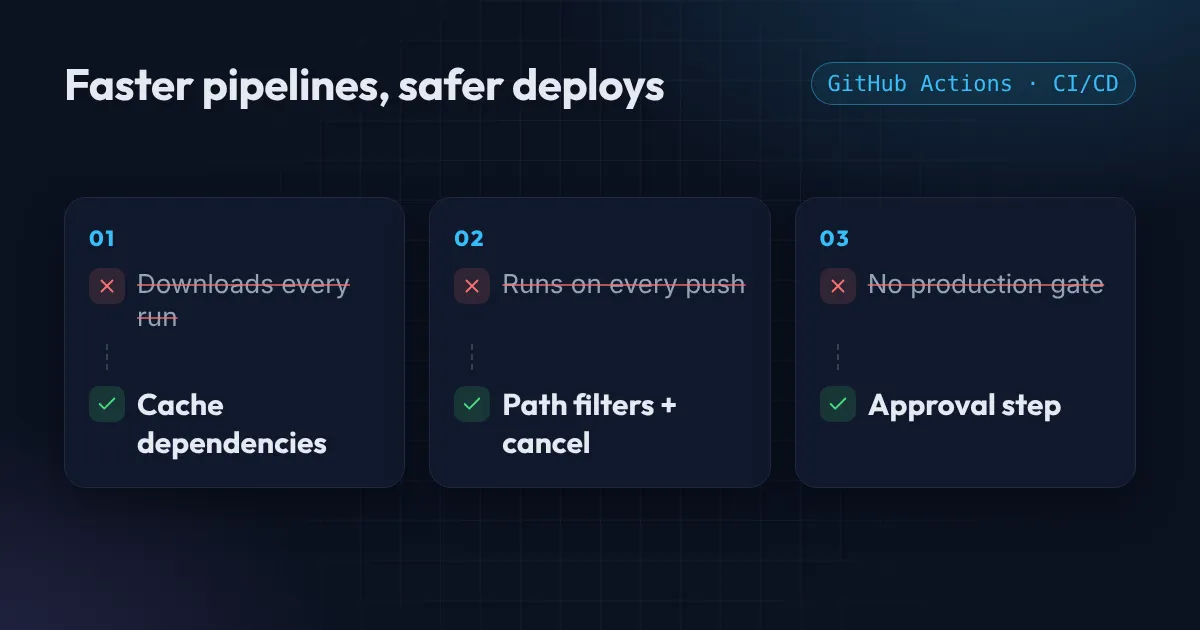
Why your GitHub Actions pipeline is slow, and the fix
GitHub Actions slow? Cache your dependencies, run only when the right files change, cancel stale runs, and put a real gate in front of production.
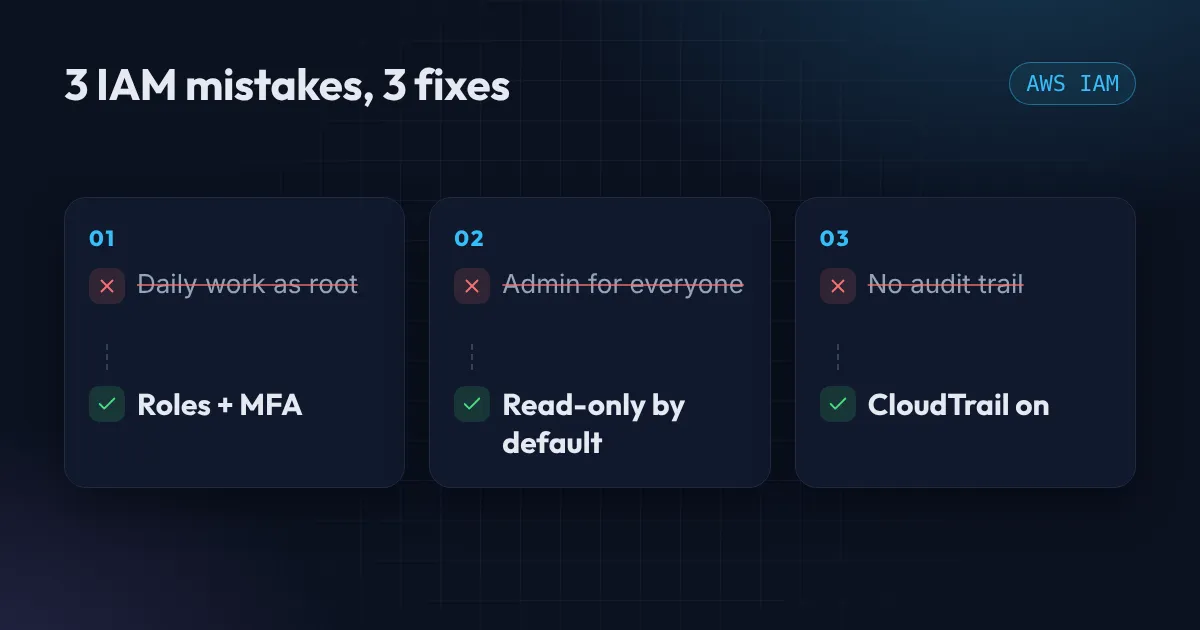
3 AWS IAM mistakes I find in almost every account
Three AWS IAM mistakes in most accounts: daily work as root, admin rights for everyone, no audit trail. The fixes: roles with MFA, read-only, CloudTrail.
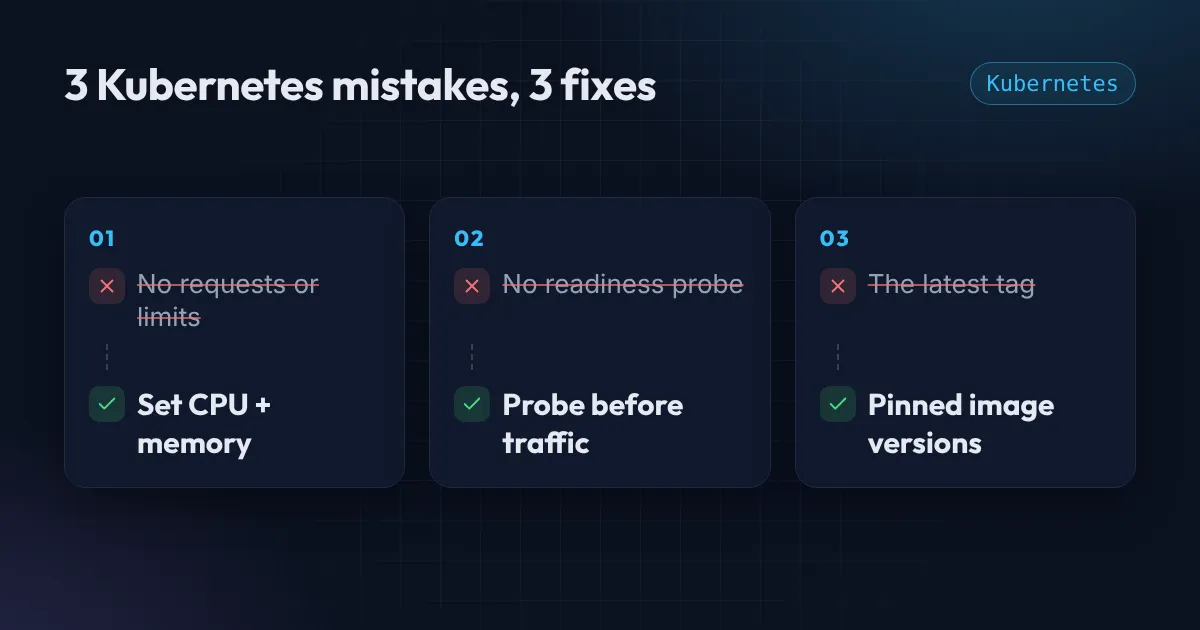
3 Kubernetes mistakes that crash your pods (and the fix for each)
Three Kubernetes mistakes behind real outages: missing resource requests and limits, no readiness probe, and the latest image tag. Each is a few lines to fix.
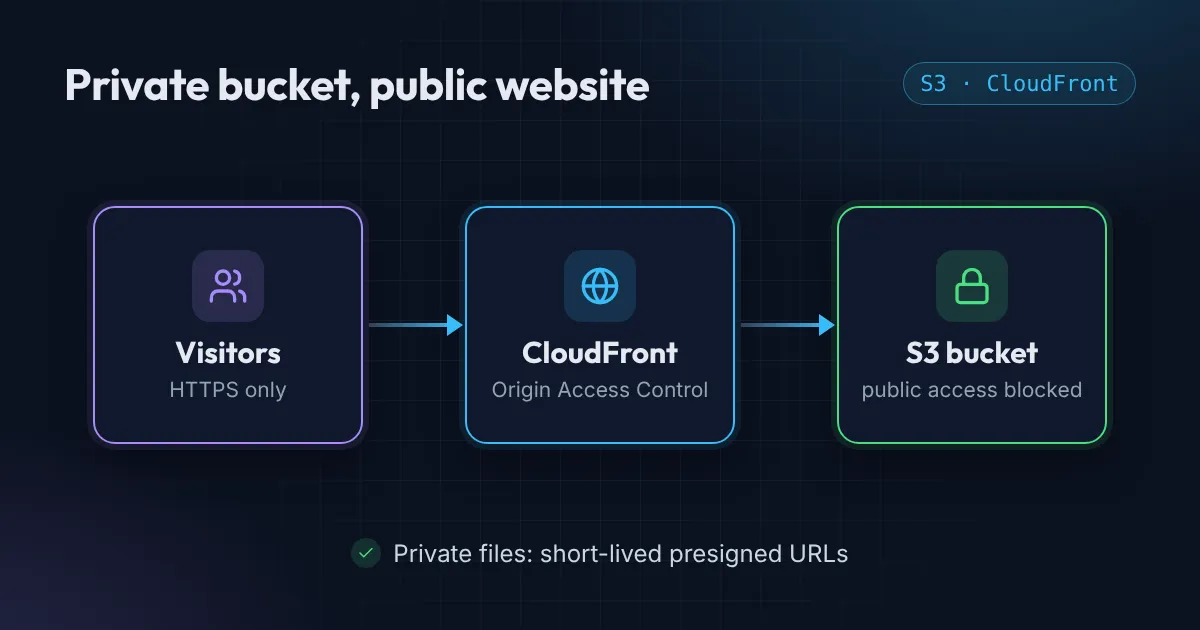
S3 Block Public Access: why a bucket should never be public
Public S3 buckets keep making headlines. My three-step setup instead: S3 Block Public Access, CloudFront with Origin Access Control, presigned URLs.
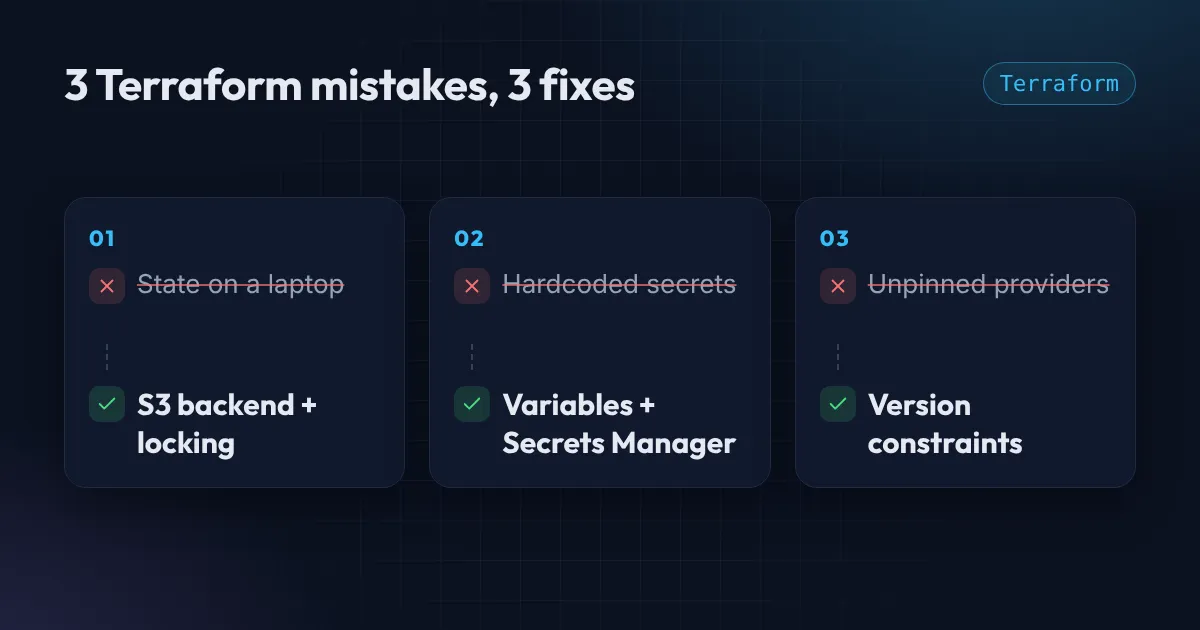
3 Terraform mistakes that cost me hours
Three Terraform mistakes that cost me hours: local state, hardcoded secrets and unpinned providers. What each one cost and the small fix that prevents it.
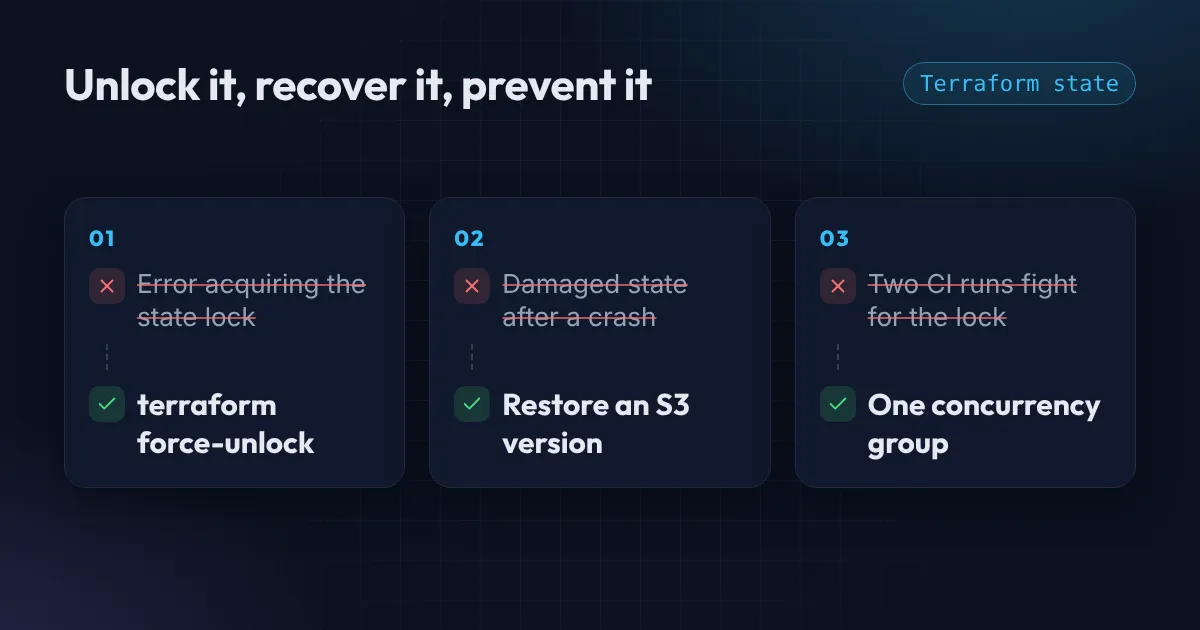
How to unlock Terraform state (force-unlock) and recover it
Stuck on "Error acquiring the state lock"? Find the lock ID, check it is safe, run terraform force-unlock, and roll back a bad state from S3 versioning.
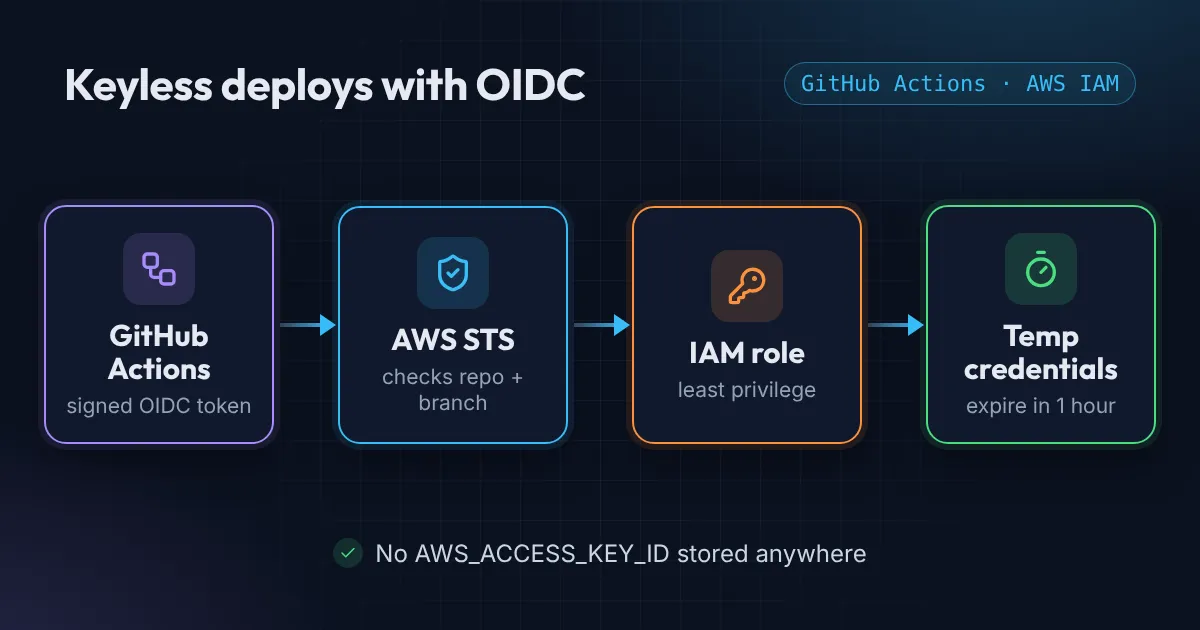
Deploy to AWS from GitHub Actions without access keys (OIDC)
Stop storing AWS keys in GitHub secrets. With GitHub Actions and AWS OIDC, each workflow run gets short-lived credentials for a locked-down IAM role.
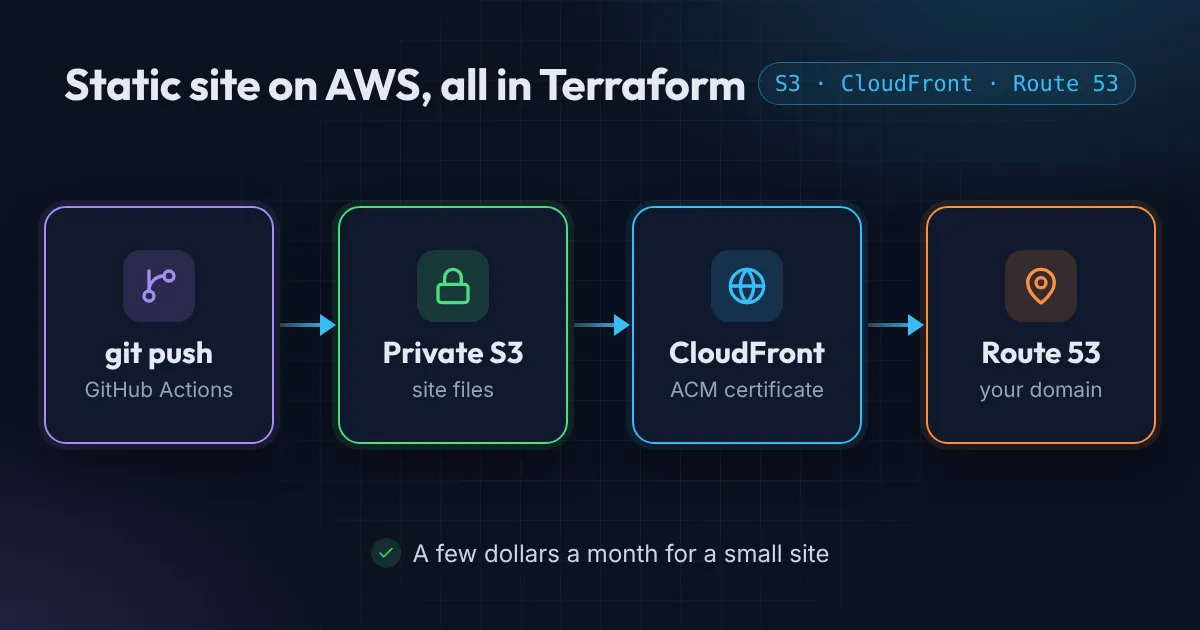
Host a static website on AWS S3 + CloudFront with Terraform
A private S3 bucket, CloudFront with Origin Access Control, a free ACM certificate and Route 53 records, all in Terraform. The exact setup behind this site.
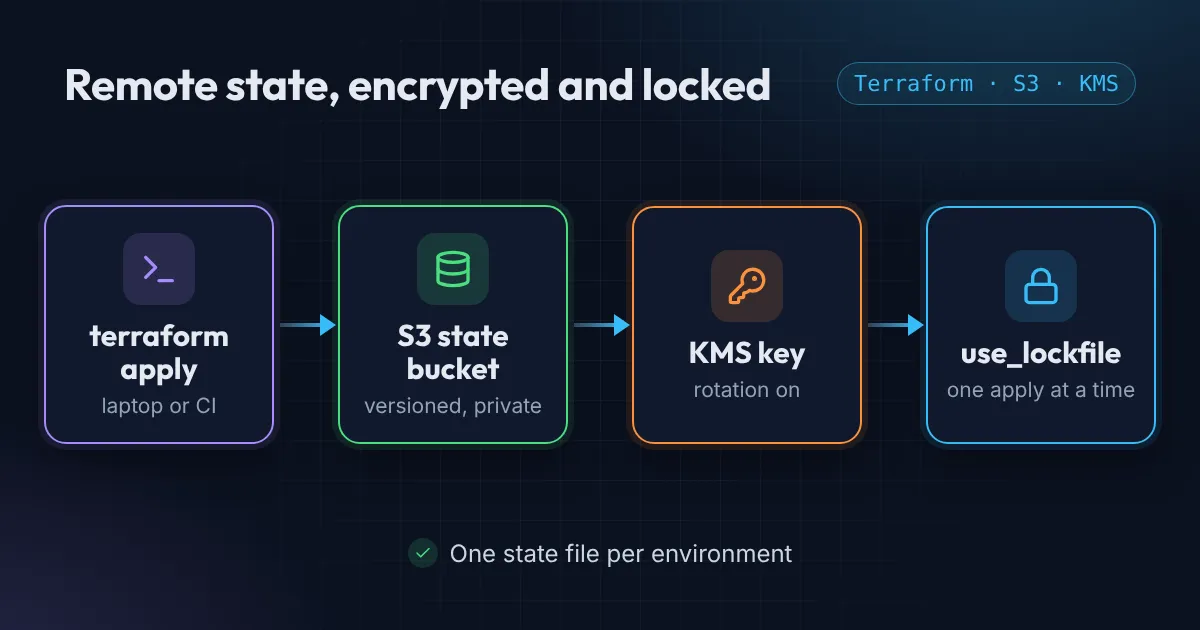
Terraform S3 backend: remote state with KMS and state locking
Set up a Terraform S3 backend for remote state: an encrypted, versioned bucket with a KMS key, native state locking, and a clean layout per environment.
Practical DevOps, once or twice a month
New tutorials, Terraform snippets and AWS cost tips. No spam, unsubscribe anytime.