Terraform on AWS: state, mistakes and real setups
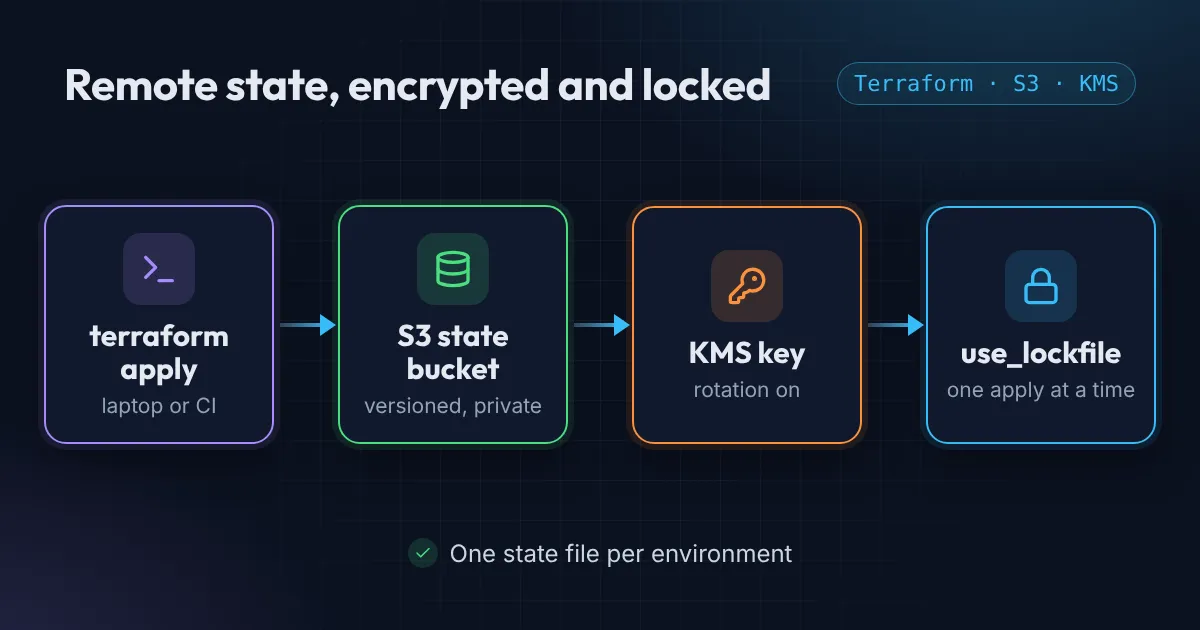
Terraform is only as safe as its state. Get the state into an encrypted, versioned S3 bucket with locking first, and most of the scary Terraform stories never happen to you.
After that, learn what to do when a lock gets stuck or a state file gets damaged, avoid the beginner mistakes that cost hours, and copy two complete setups: a static website on S3 and CloudFront, and a VPC with room to grow.
Then read
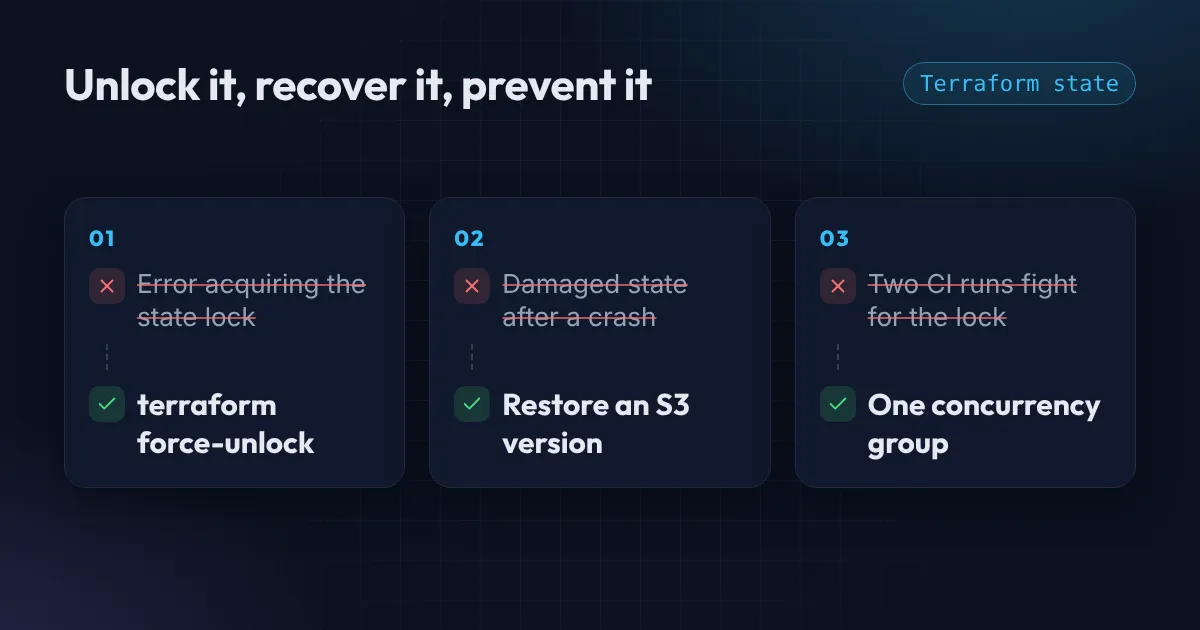
How to unlock Terraform state (force-unlock) and recover it
Stuck on "Error acquiring the state lock"? Find the lock ID, check it is safe, run terraform force-unlock, and roll back a bad state from S3 versioning.
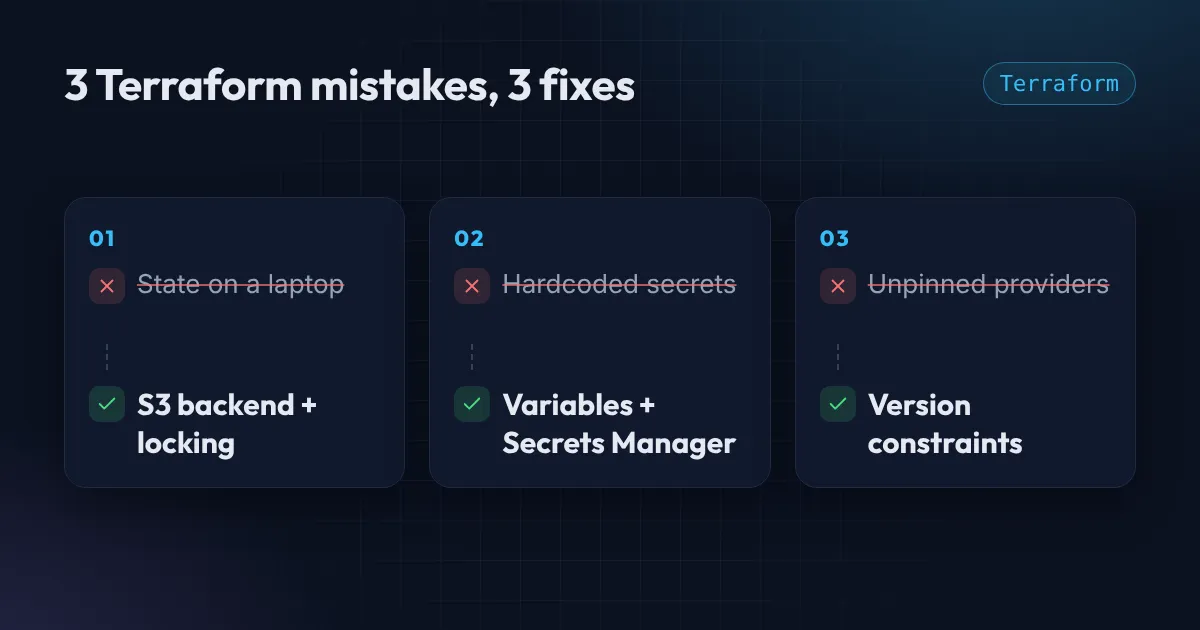
3 Terraform mistakes that cost me hours
Three Terraform mistakes that cost me hours: local state, hardcoded secrets and unpinned providers. What each one cost and the small fix that prevents it.
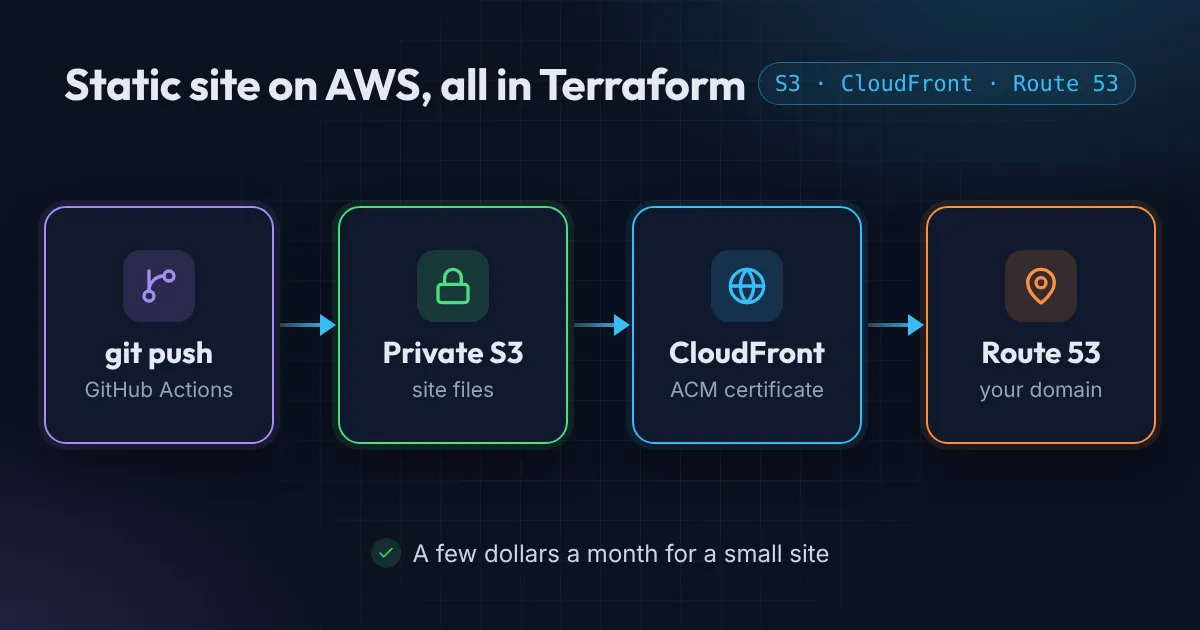
Host a static website on AWS S3 + CloudFront with Terraform
A private S3 bucket, CloudFront with Origin Access Control, a free ACM certificate and Route 53 records, all in Terraform. The exact setup behind this site.
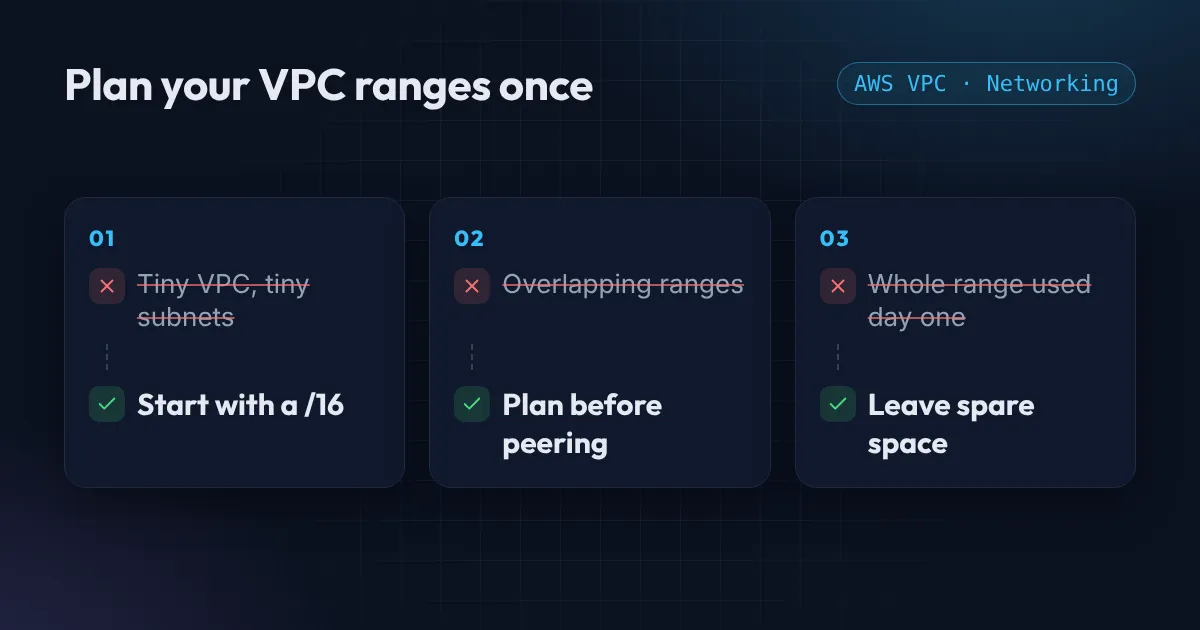
How to plan VPC CIDR ranges so you never have to rebuild
VPC CIDR planning in plain steps: pick a range and subnet sizes that leave room to grow, avoid overlaps, and allow for the 5 IPs AWS reserves per subnet.
Tools and checklists
- VPC CIDR and subnet calculatorPlan subnets before you write the Terraform.
Rather have it done for you?
Click-built AWS accounts turned into reviewed, repeatable Terraform.
Other guides
Practical DevOps, once or twice a month
New tutorials, Terraform snippets and AWS cost tips. No spam, unsubscribe anytime.