AWS security for small teams: IAM, S3 and secrets
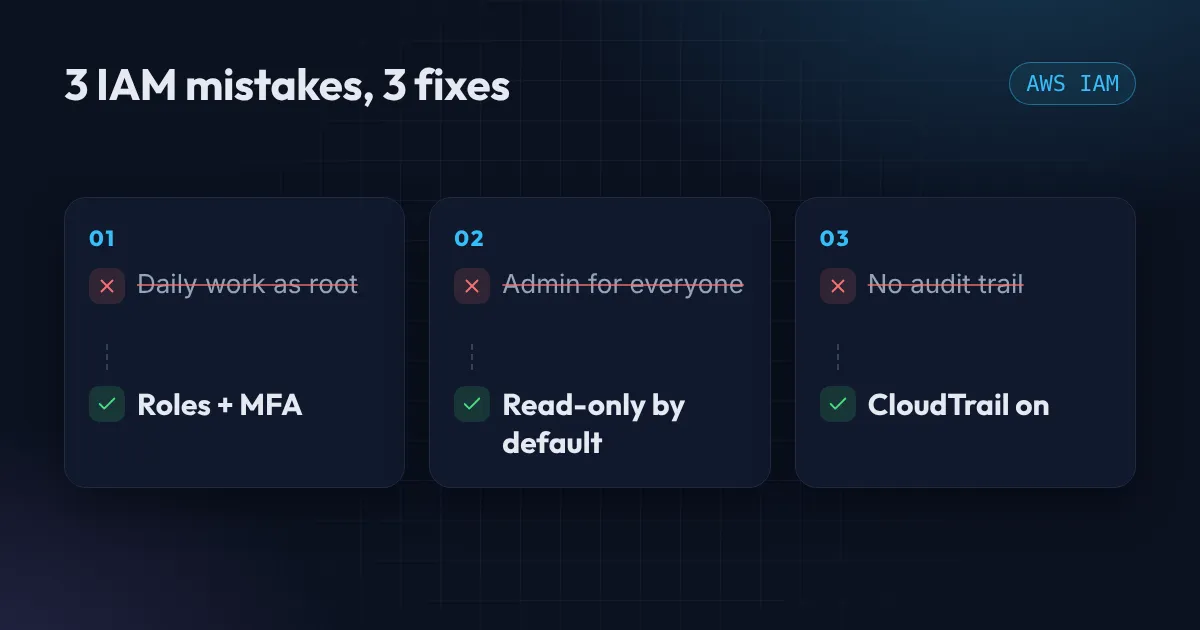
Most AWS breaches at small companies start with something simple: a root account used every day, an admin role for everyone, a public bucket, or a secret that was only Base64 encoded.
Fix IAM first, because it controls everything else. Then lock down S3, remove access keys from CI, and check that your secrets are really encrypted. The checklist and policy checker help you verify each step.
Then read
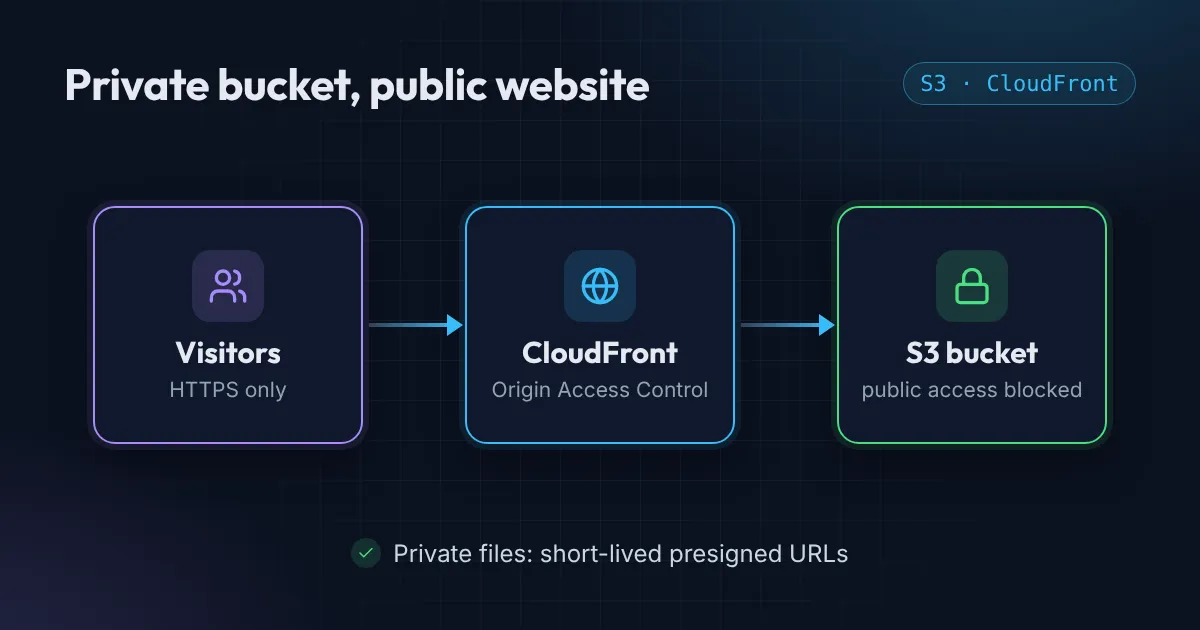
S3 Block Public Access: why a bucket should never be public
Public S3 buckets keep making headlines. My three-step setup instead: S3 Block Public Access, CloudFront with Origin Access Control, presigned URLs.
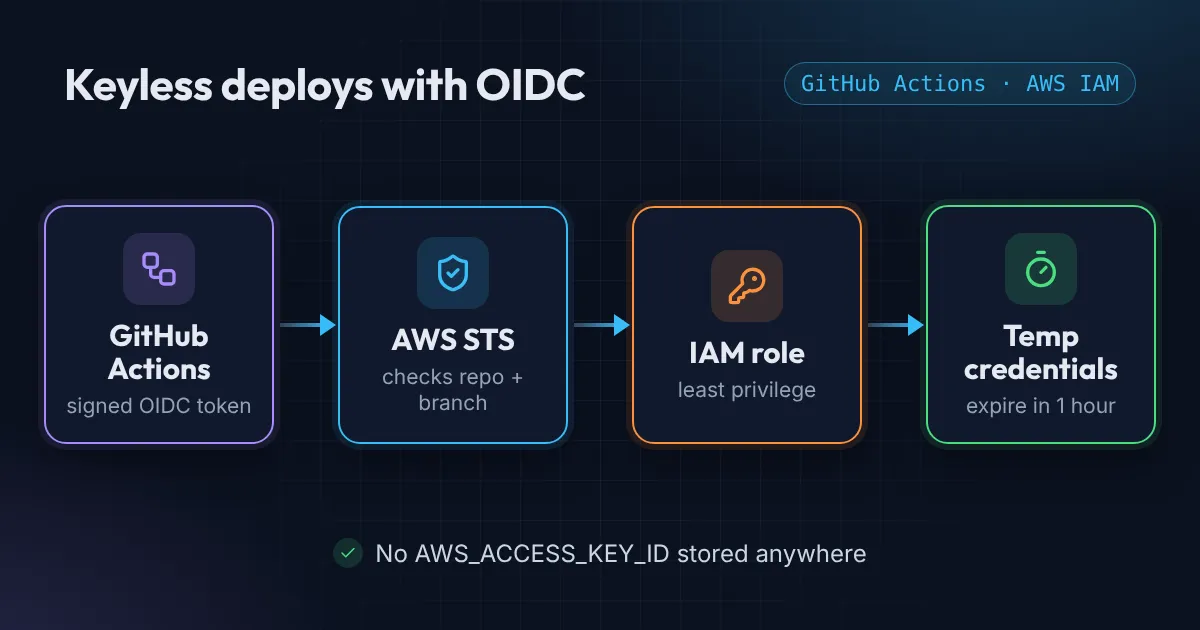
Deploy to AWS from GitHub Actions without access keys (OIDC)
Stop storing AWS keys in GitHub secrets. With GitHub Actions and AWS OIDC, each workflow run gets short-lived credentials for a locked-down IAM role.
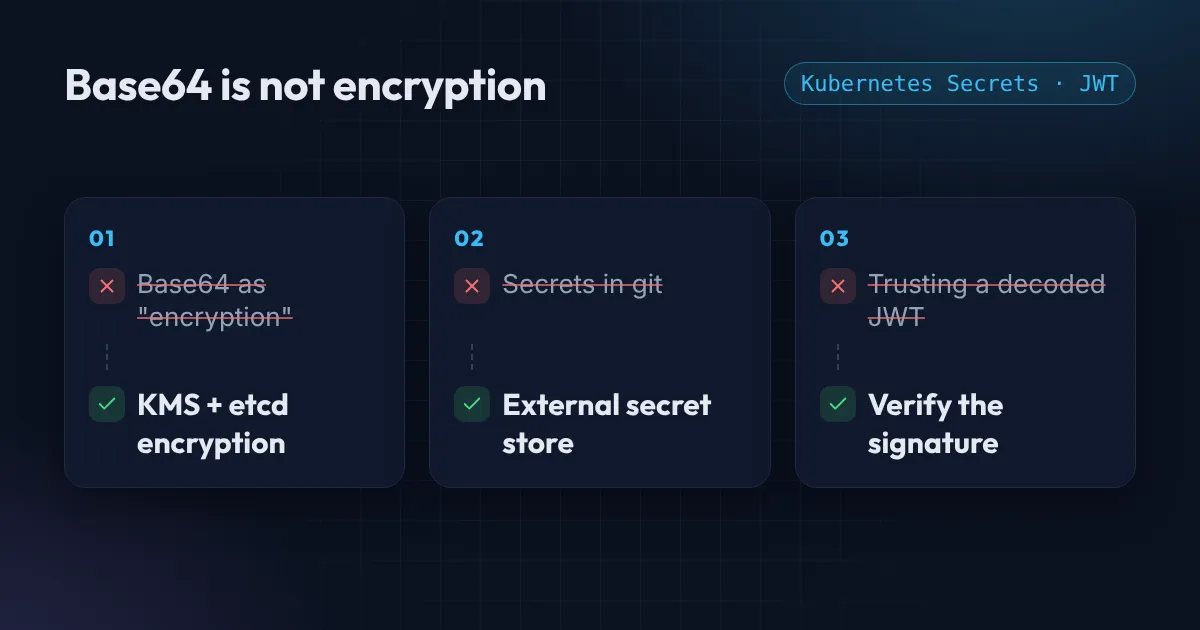
Base64 is not encryption: Kubernetes Secrets and JWT mistakes
Base64 is encoding, not encryption, so Kubernetes Secrets and JWT payloads are readable by anyone. What that means, how to decode safely, and safer options.
Tools and checklists
- S3 security checklist20 checks for every bucket.
- IAM and S3 policy checkerPaste a policy, see the risky lines.
- Base64 and JWT decoderSee what a token really contains.
Rather have it done for you?
Send me your setup and I will list the security fixes worth doing first.
Other guides
Practical DevOps, once or twice a month
New tutorials, Terraform snippets and AWS cost tips. No spam, unsubscribe anytime.