GitHub Actions CI/CD setup that deploys safely
Push to main, tests run, the app deploys. I set up GitHub Actions CI/CD pipelines that are fast, keep no long-lived AWS keys, and are easy for your team to read and change.
CI/CD pipelines: problems I fix
Deploys are manual and scary
If deploying means one person running commands from a laptop, you have a bus-factor problem. I make it a button-free, repeatable process.
AWS keys sit in CI secrets
Long-lived keys are a leak waiting to happen. I replace them with OIDC, so the pipeline gets short-lived access that only your repository can use.
The pipeline is slow
Caching, parallel jobs and cutting unneeded steps often turn a long wait into a short one.
No safety net
I add a health check after each deploy and write down the rollback steps, so a bad release is a short problem.
What is included
- Build, test and deploy stages in your repository
- Keyless AWS login with OIDC and a least-privilege role
- Separate environments where you need them
- Post-deploy check and documented rollback
- A handover walkthrough
Fixed price: CI/CD Pipeline, from $300, typical delivery 3–5 days. Smaller job? Pipeline fix, from $90. See all packages and pricing
permissions:
  id-token: write
  contents: read

steps:
  - uses: actions/checkout@v6
  - uses: aws-actions/configure-aws-credentials@v6
    with:
      role-to-assume: arn:aws:iam::123456789012:role/deploy-role
      aws-region: us-east-1
  - run: aws s3 sync dist s3://my-site-bucket --delete
What clients say
I requested an integration with Github actions and terraform for an automation CI/CD setup, Cloud guru was able to deliver even though it was not included in the package. It was delivered in time and he was able to demonstrate how to go about running the scripts.
Umar did a great job setting up the AWS infrastructure for my website. Everything was done with Terraform S3, CloudFront, Route 53, ACM, and a GitHub Actions pipeline. The site is live over HTTPS and deploys automatically on every push. Code was clean and the README made it easy to understand. Negotiated fairly on price and delivered on time. Would hire again.
Guides on this topic
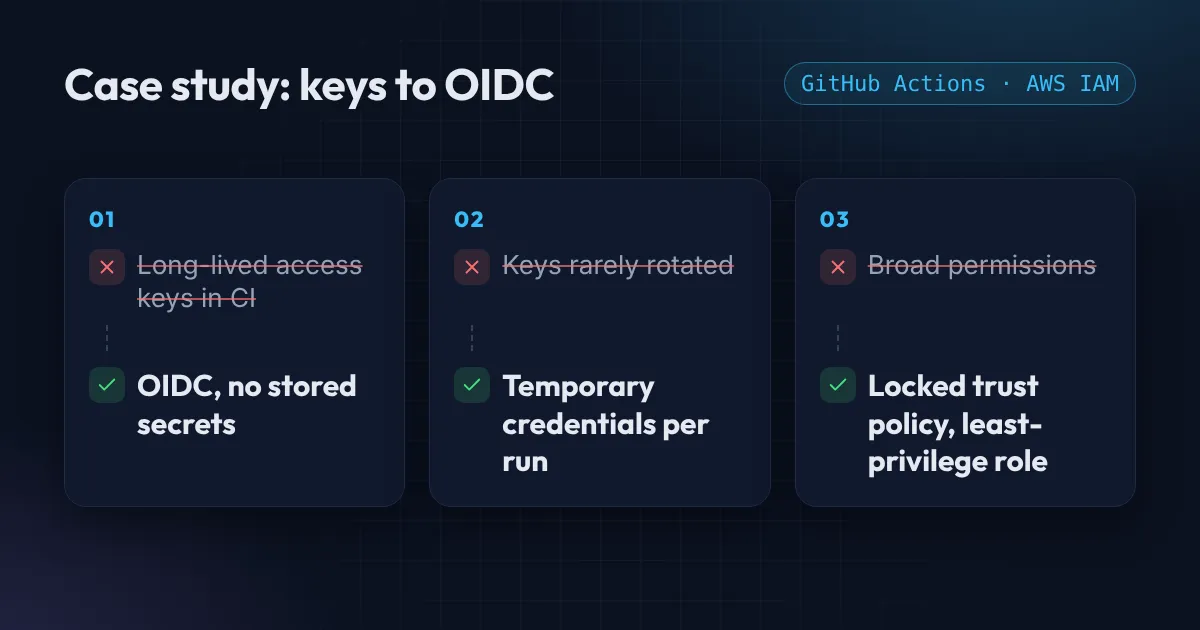
Case study: GitHub Actions OIDC replaced a startup's AWS keys
A GitHub Actions OIDC case study: a small team kept long-lived AWS keys in CI and never rotated them. How I moved them to OIDC in one day, and what changed.
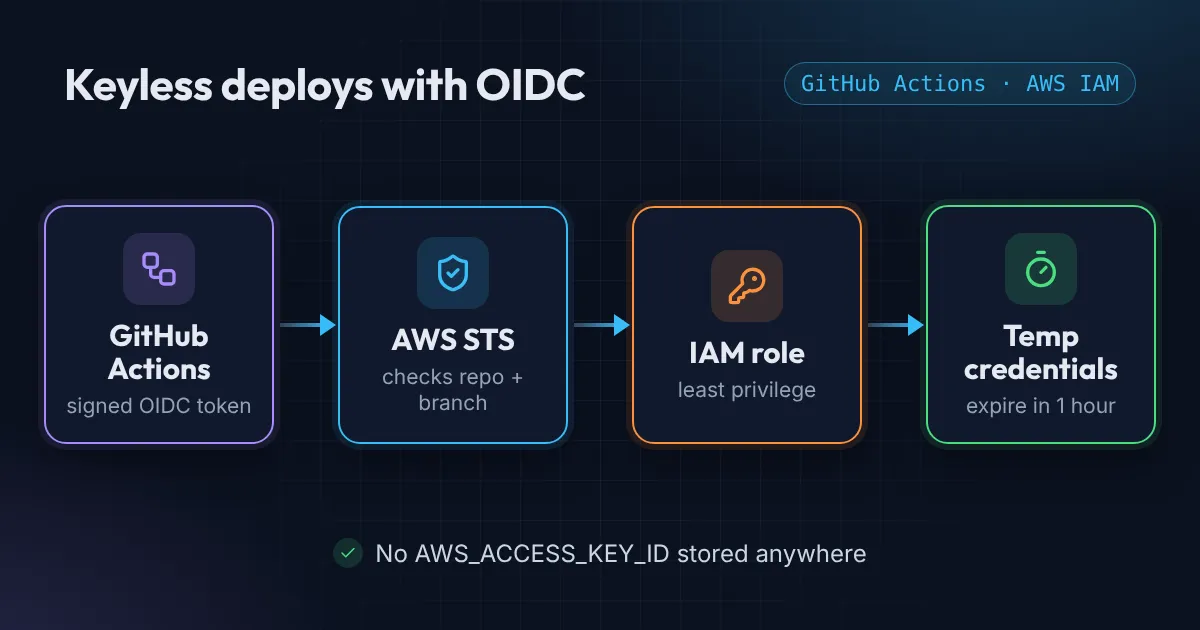
Deploy to AWS from GitHub Actions without access keys (OIDC)
Stop storing AWS keys in GitHub secrets. With GitHub Actions and AWS OIDC, each workflow run gets short-lived credentials for a locked-down IAM role.
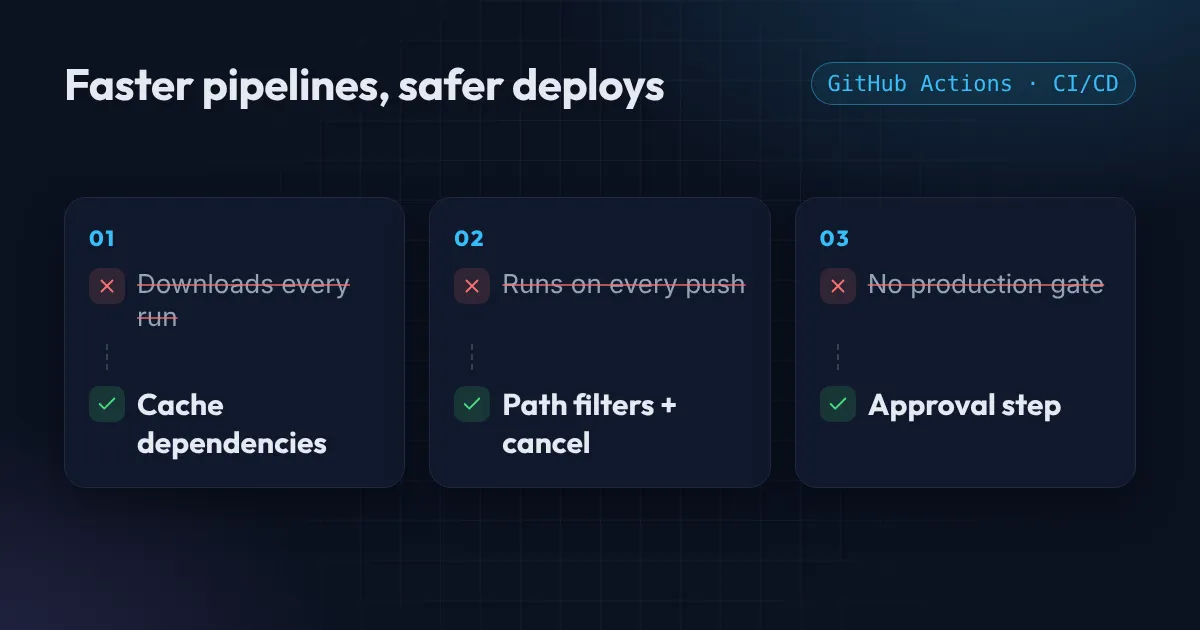
Why your GitHub Actions pipeline is slow, and the fix
GitHub Actions slow? Cache your dependencies, run only when the right files change, cancel stale runs, and put a real gate in front of production.
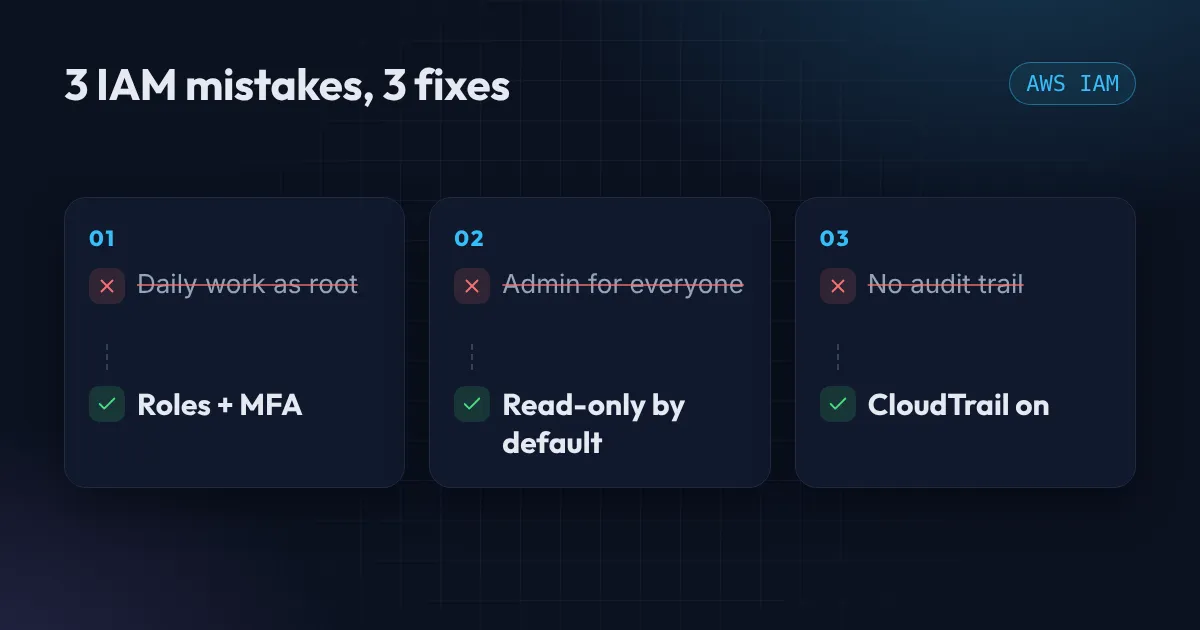
3 AWS IAM mistakes I find in almost every account
Three AWS IAM mistakes in most accounts: daily work as root, admin rights for everyone, no audit trail. The fixes: roles with MFA, read-only, CloudTrail.
GitHub Actions, GitLab CI or Jenkins?
GitHub Actions is my default. I also set up GitLab CI and Jenkins pipelines, so I follow what your team already uses.
Can you fix a pipeline that already exists?
Yes. The pipeline fix add-on covers one existing pipeline: finding what is slow or broken and fixing it.
Where can the pipeline deploy to?
S3 and CloudFront, ECS, EKS or EC2, depending on how your app runs.
What about secrets?
Secrets stay in your secret store or GitHub secrets. With OIDC there are no AWS keys to store at all.
Other services
Freelance Terraform consultant for AWS teams
As a freelance Terraform consultant, I turn click-built AWS accounts into reviewed, repeatable Terraform, and write new infrastructure as clean modules your team can keep using after I leave.
AWS cost optimization consultant for startups
Most AWS bills have waste nobody has looked for. As your AWS cost optimization consultant, I review your account, find what you are paying for but not using, and give you a short written list of fixes in order of savings.
EKS setup consultant: Kubernetes done properly
As an EKS setup consultant, I containerize your app and run it on EKS or another managed cluster, with Terraform for the cluster, Helm for the apps, and monitoring so you hear about problems first.
Not sure where to start?
Send me a short description of your setup and I'll tell you what to fix first. Free.
Get a Free AWS Review